Cybersecurity · Network Analysis
WireTally
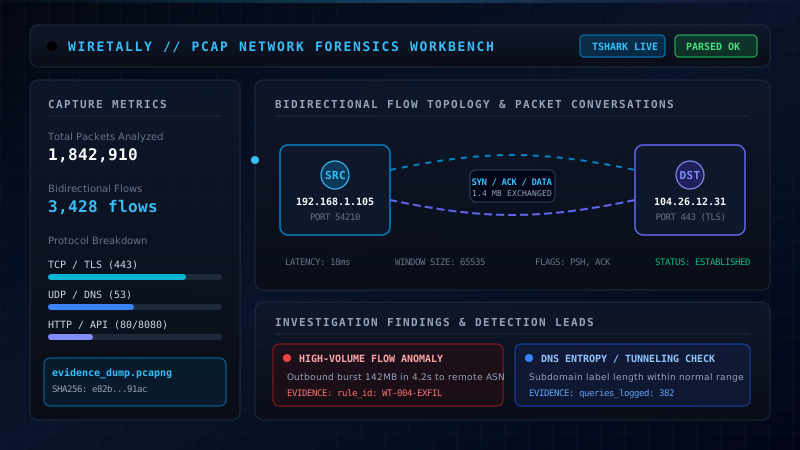
WireTally reads authorized PCAP/PCAPNG files, leverages TShark to extract selected packet metadata, aggregates TCP/UDP packets into bidirectional flows, applies transparent rules, and writes structured JSON evidence reports.
Features
- Validates local PCAP and PCAPNG files (type, size limit, empty files) before analysis
- Extracts packet metadata with TShark and aggregates bidirectional TCP and UDP flows
- Two transparent detection rules: high-volume transfers and flows on selected suspicious ports
- Timestamped JSON evidence report that includes observed DNS query names
- Three interfaces: CLI, local FastAPI endpoint and a React and TypeScript UI
Technologies
PythonTSharkPCAP/PCAPNGFastAPIReactTypeScriptViteJSON